Upgrade to laravel/framework 13.43.0 (released 17 Nov 2026), or 12.73.0 if you are still on 12.x. Both carry a batch of security fixes that shipped without CVE IDs: temporary signed URLs that could outlive their expires time, a mass-assignment guard that could be sidestepped through mutator name normalisation, XSS in Blade component attributes and in the debug page, a file validation bypass, and a depth limit for $ref chains in the JSON Schema deserializer. If your app uses URL::temporarySignedRoute(), a $guarded denylist, or $attributes->merge() with object values, those paths are the ones to check first.
Why we did this: two of the Laravel apps we run, BMDB and SBTV, are on Laravel 13 after their upgrade hops from 10 and 9, and both send temporary signed links. We read every pull request behind the release, built the table below from the diffs, and wrote a small audit script that finds the affected code paths in an app.
What 13.43.0 fixes, in one table
Every fix was merged into the 12.x branch first and reached 13.x through branch merges, so the 12.x version is listed too. Versions come from the pull requests and the release notes.
| Fix | File | What changed | First 12.x | PR |
|---|---|---|---|---|
Signed URL expires read from the raw query string |
Routing/UrlGenerator.php |
Falls back to parsing the raw query when expires is missing |
12.72.0 | #62349 |
| Same, for Vapor’s raw query string | Routing/UrlGenerator.php |
Reads VAPOR_RAW_QUERY_STRING when present |
12.72.0 | #62391 |
| Numeric route parameters in signed URLs | Routing/RouteUrlGenerator.php |
Unkeyed parameters are rawurlencoded |
12.72.0 | #62401 |
Array expires values |
Routing/UrlGenerator.php |
A non-string expires fails the check |
12.73.0 | #62411 |
| Regression from #62401 | Routing/RouteUrlGenerator.php |
EncodedParameter values are not encoded twice |
12.73.0 | #62417 |
| Mass-assignment guard and mutators | Eloquent/Concerns/GuardsAttributes.php |
isGuarded() also compares studly-cased names |
12.73.0 | #62499 |
| XSS in component attributes | View/ComponentAttributeBag.php |
Object defaults are escaped unless they are Htmlable |
12.73.0 | #62503 |
| XSS in the debug page’s copy-URL button | exceptions/renderer/components/request-url.blade.php |
URL passed through Js::from() |
12.73.0 | #62418 |
| File validation with a same-named empty field | Http/Concerns/InteractsWithInput.php |
A blank input value no longer hides the uploaded file | 12.73.0 | #62504, #62521 |
Unbounded $ref chains |
JsonSchema/Deserializer.php |
Depth capped at 64, then InvalidArgumentException |
12.73.0 | #62498 |
Two packaging notes from the release: composer.json now declares a conflict with laravel/horizon below 5.47.0 (#62449), so update Horizon in the same composer update, and the Markdown mail escaping fix that appears in the 12.x merge list (#62027) already shipped in 13.36.0 in October.
Temporary signed URLs
Five pull requests touch the same feature. Before them, signatureHasNotExpired() read expires from the parsed query and compared it to the current time. The fixes make the check stricter in three ways: a non-string expires (for example an array) now fails, expires is re-read from the raw query string when the parsed value is missing, and unkeyed route parameters are URL-encoded so they cannot change how the query string is parsed.
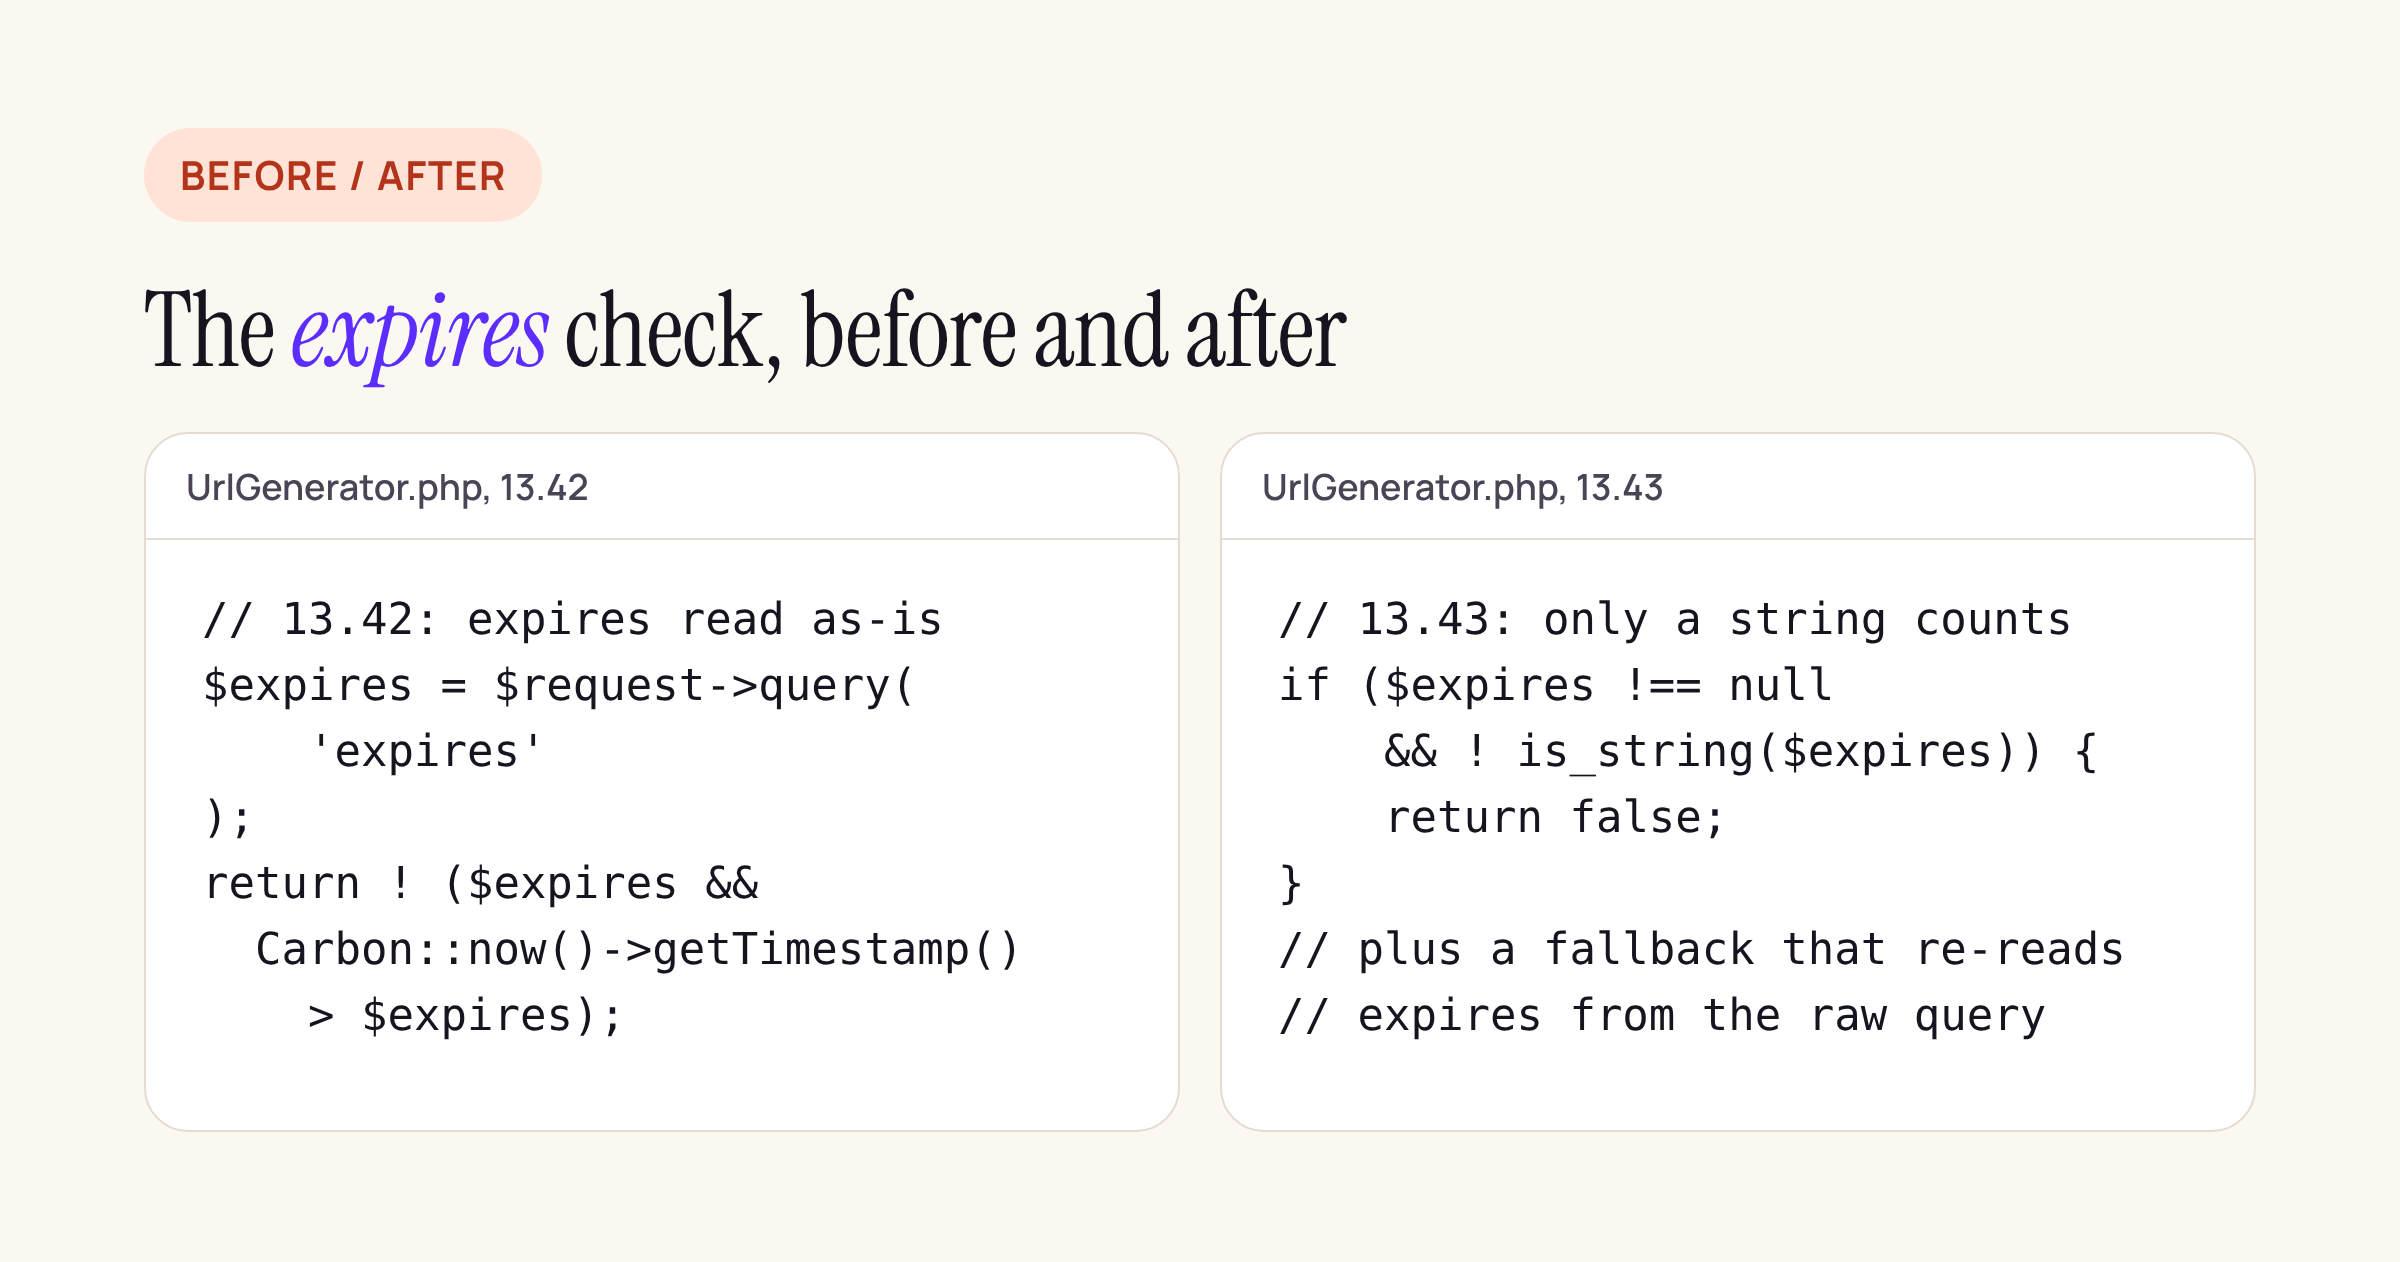
The 13.42 side is the long-standing check; the 13.43 side is the guard added in #62411.
We extracted the new type check into a standalone script and ran it against three values: an expired timestamp, a valid one, and the same expired timestamp wrapped in an array.
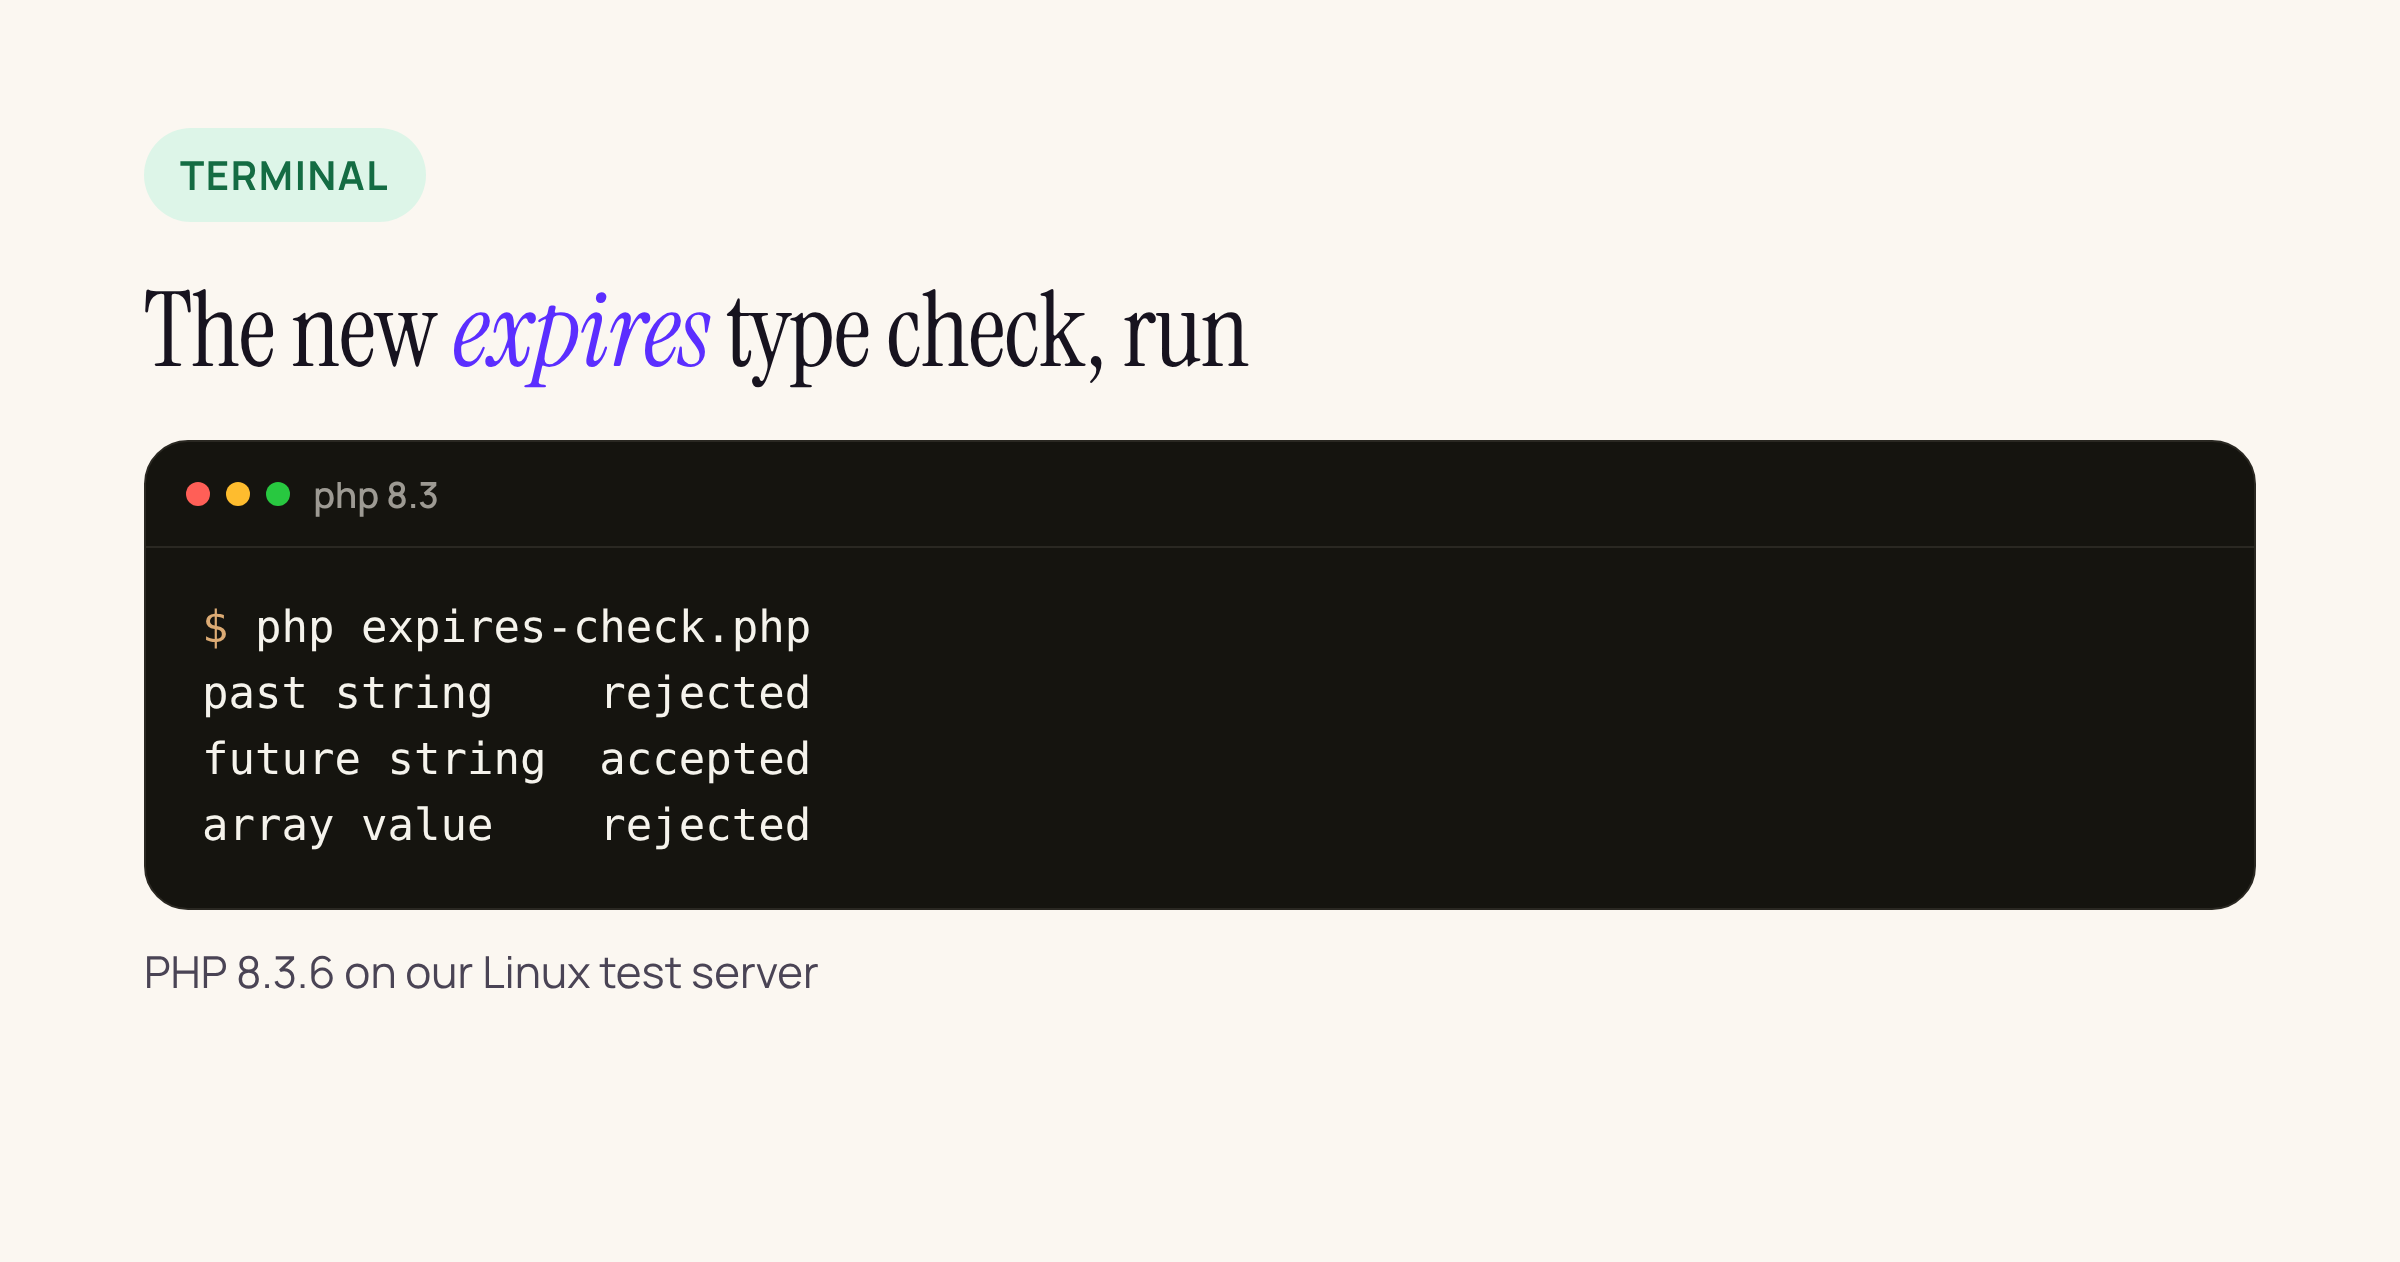
Both the expired string and the array value are rejected; only the valid string passes.
You are exposed if your app uses URL::temporarySignedRoute() or URL::temporarySignedUrl() with the signed middleware or hasValidSignature() and relies on the expiry for access control: download links, email verification, unsubscribe links, password-reset style flows. Apps on Vapor or behind a proxy that rewrites query strings get the raw-query fallback from #62391. If expiry mattered for access, it is worth checking your access logs for signed-route hits with an expires value that is not a plain timestamp.
Mass assignment through a mutator name
isGuarded() matched the incoming key against the $guarded list with a case-insensitive regex. #62499 adds a second comparison after Str::studly() on both sides, so different spellings of the same attribute name map to the same guarded entry. The PR’s comment calls out the mismatch between how the guard compared names and how mutators normalise them.
// GuardsAttributes::isGuarded(), 13.43.0 (excerpt)
$normalizedKey = Str::studly($key);

foreach ($this->getGuarded() as $guardedKey) {
    if (preg_match('/^'.preg_quote($key, '/').'$/i', $guardedKey) ||
        preg_match('/^'.preg_quote($normalizedKey, '/').'$/i', Str::studly($guardedKey))) {
        return true;
    }
}

return ! $this->isGuardableColumn($key);
You are exposed if all three are true: a model uses a $guarded denylist (not $fillable, and not ['*']), the guarded attribute has a mutator (setXAttribute() or an Attribute accessor with a setter), and the model is filled from unfiltered input such as $request->all(). Using $fillable, or fill($request->validated()), closes this path on any version.
Two XSS fixes in Blade
Component attributes (#62503). ComponentAttributeBag::merge() skipped escaping for any object default. A Stringable built with str($input) therefore went into the HTML unescaped. Now only Htmlable values (and null or booleans) skip escaping. Check components that pass str() results or other __toString() objects built from user data into $attributes->merge([...]).
The debug page (#62418). The exception page’s “copy request URL” button wrote the URL into a JavaScript string with {{ }}. It now uses Js::from(). This only matters where the exception page renders, so APP_DEBUG=true: a misconfigured production server, a shared staging site, or a developer opening a link someone sent them.
{{-- request-url.blade.php, 13.43.0 --}}
await window.copyToClipboard({{ Illuminate\Support\Js::from($request->fullUrl()) }});
File validation and JSON Schema
File validation (#62504 on 12.x, #62521 on 13.x). When a text field and an uploaded file had the same name, the text value won when input and files were merged, even if it was empty. Validation saw the empty value while $request->file() still returned the upload. The new mergeFilesWithInput() lets the file win when the input value is blank. Check upload fields validated with nullable or sometimes plus file, image, mimes or max, where the code then stores $request->file(...) without another check.
JSON Schema (#62498). Illuminate\JsonSchema\Deserializer now stops after 64 nested $ref levels. Only apps that deserialize schemas from outside input are affected, for example user-supplied schemas for structured AI output.
An audit script for your app
The script below lists the code paths the fixes touch: models with a $guarded denylist and how many mutators each has, temporary signed URLs, and attribute merges in Blade components. It reads files only.
#!/usr/bin/env bash
# Where a Laravel app touches the code paths fixed in 13.43.0
cd "${1:-.}"
echo "== models with a \$guarded denylist"
grep -rln 'protected \$guarded *= *\[' app/Models | while read f; do
  m=$(grep -cE 'function set[A-Za-z]+Attribute|Attribute::make' "$f")
  echo "$f  mutators: $m"
done
echo "== temporary signed URLs"
grep -rnE 'temporarySignedRoute|temporarySignedUrl' app routes | cut -c1-60
echo "== attribute merges in Blade components"
grep -rn 'attributes->merge' resources/views | cut -c1-60
We ran it on a small fixture app with one guarded model that has a mutator, one model using $fillable, a signed download route and a badge component.
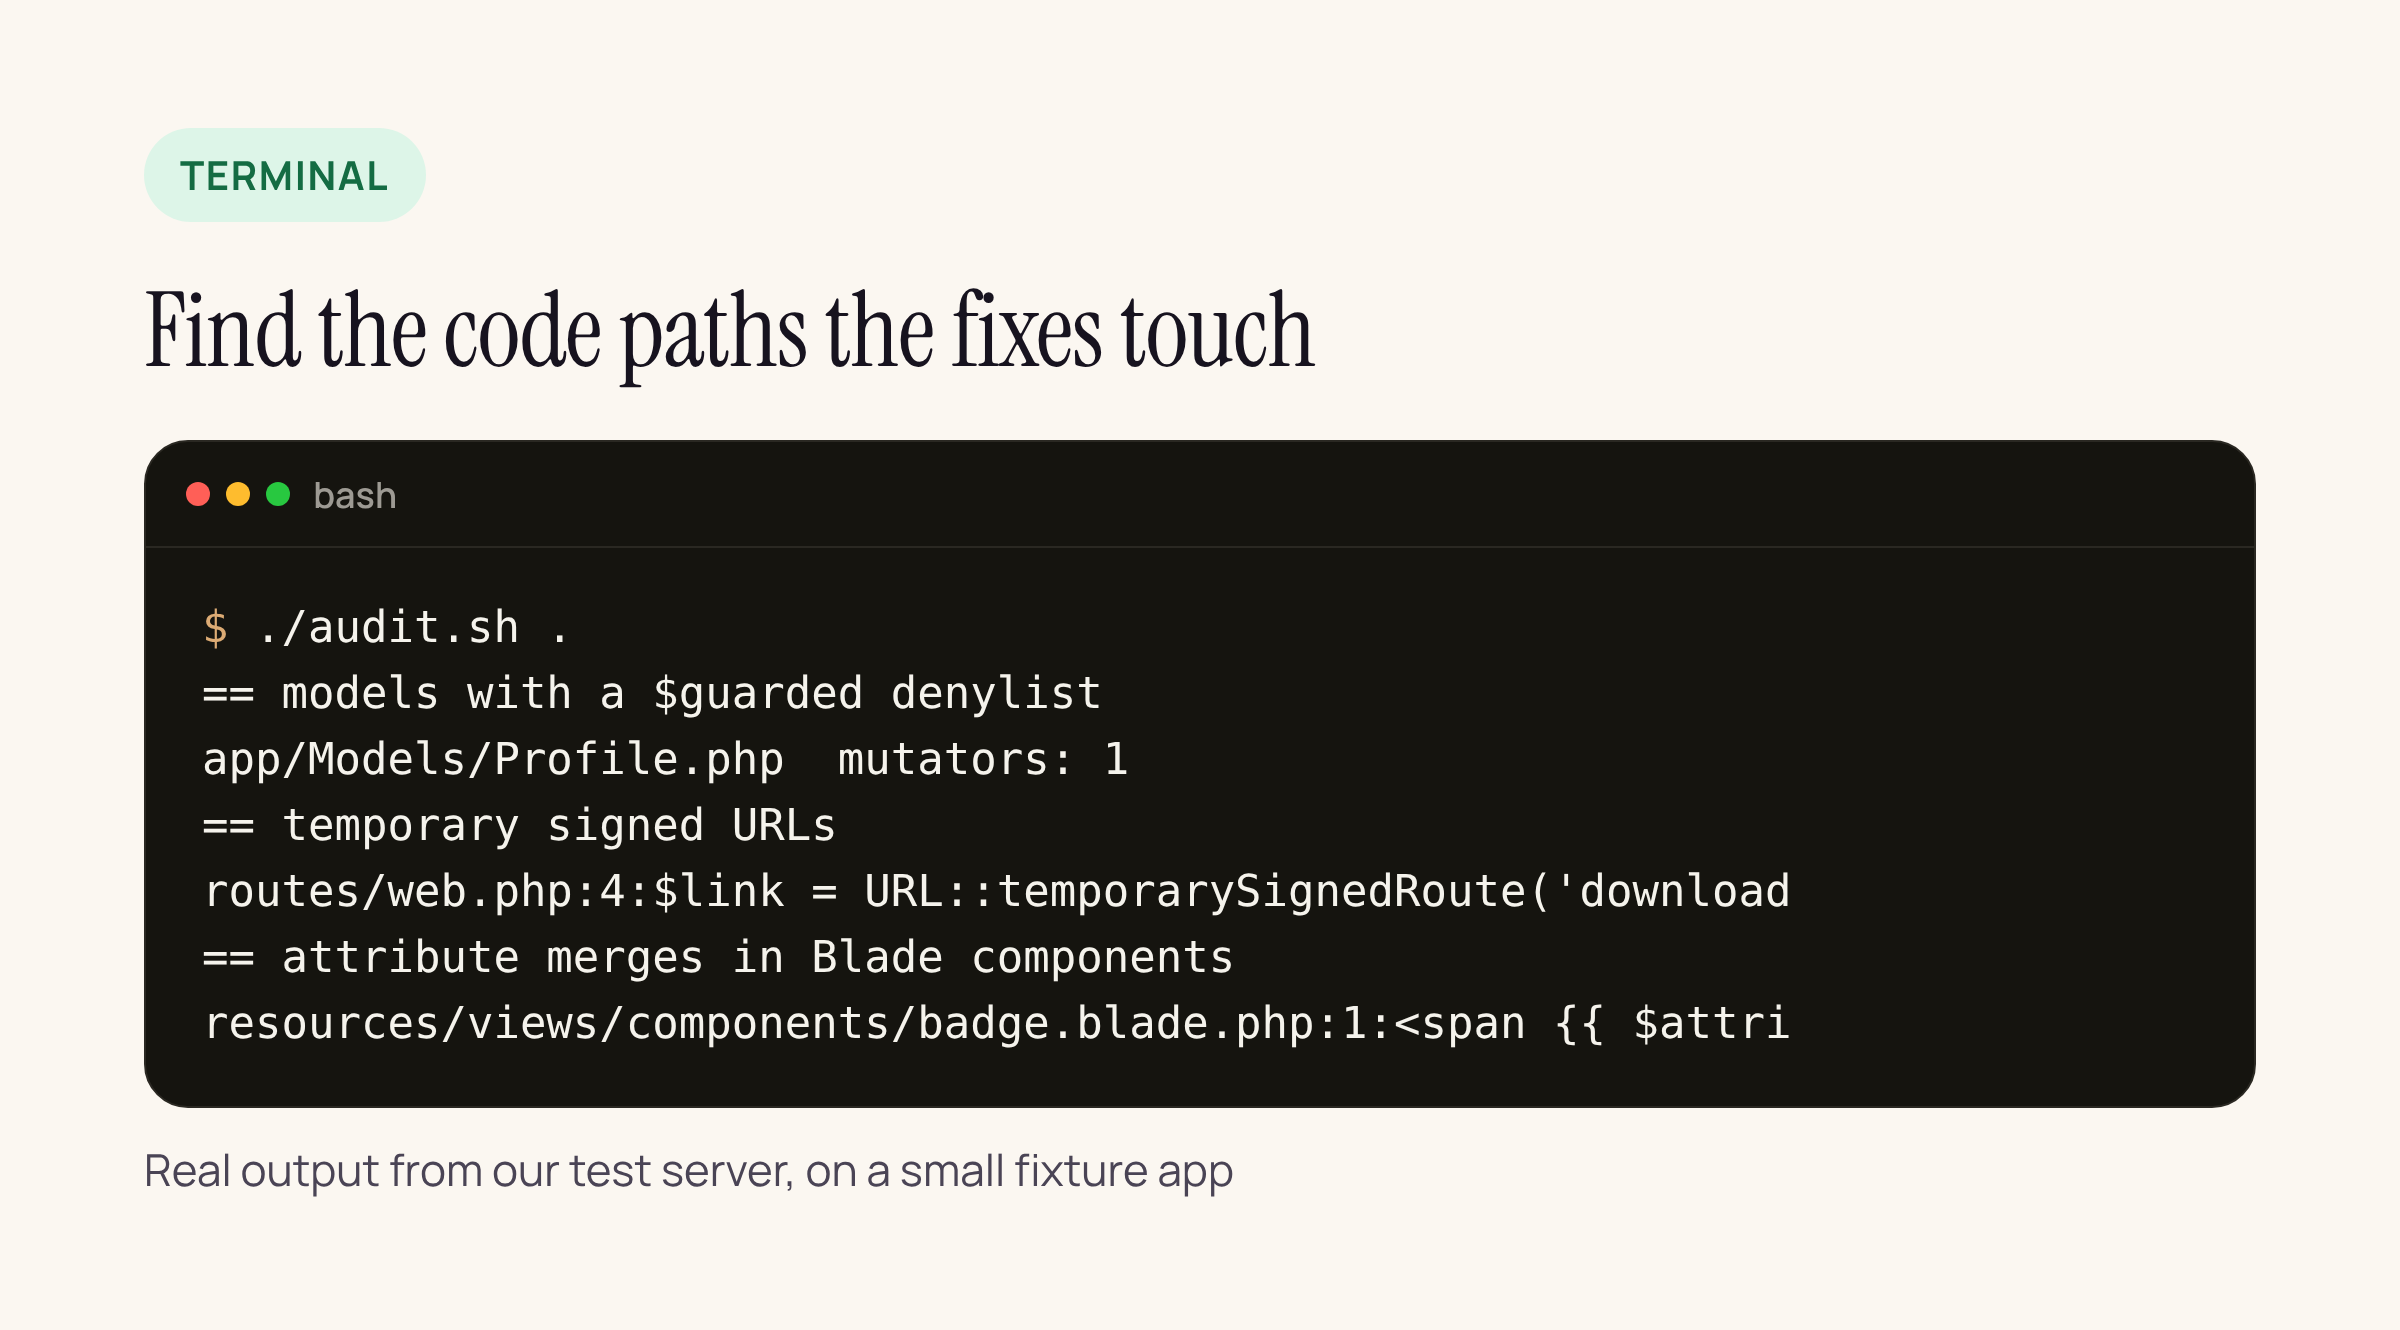
The $fillable model is not listed; the guarded model with a mutator, the signed route and the component merge are.
Upgrade steps
- Check the version you run:
composer show laravel/framework | grep versions. - Update the framework and Horizon together:
composer update laravel/framework laravel/horizon --with-dependencies. - Confirm 13.43.0 or later (12.73.0 or later on 12.x), then run your test suite. The #62401 encoding change had one regression, fixed in #62417, so a test that builds signed URLs with unkeyed parameters is worth having.
- Run the audit script and move any
$guardedmodel that is filled from request input to$fillableorvalidated()input, whatever version you are on. - Make sure
APP_DEBUGisfalseeverywhere outside a developer’s own machine.
Sources
- Laravel 13.43.0 on Laravel News (18 Nov 2026)
- laravel/framework v12.73.0 release notes and v12.72.0
- laravel/framework on Packagist (release date and the Horizon conflict)
- The pull requests linked in the table above